CVE-2018-19461
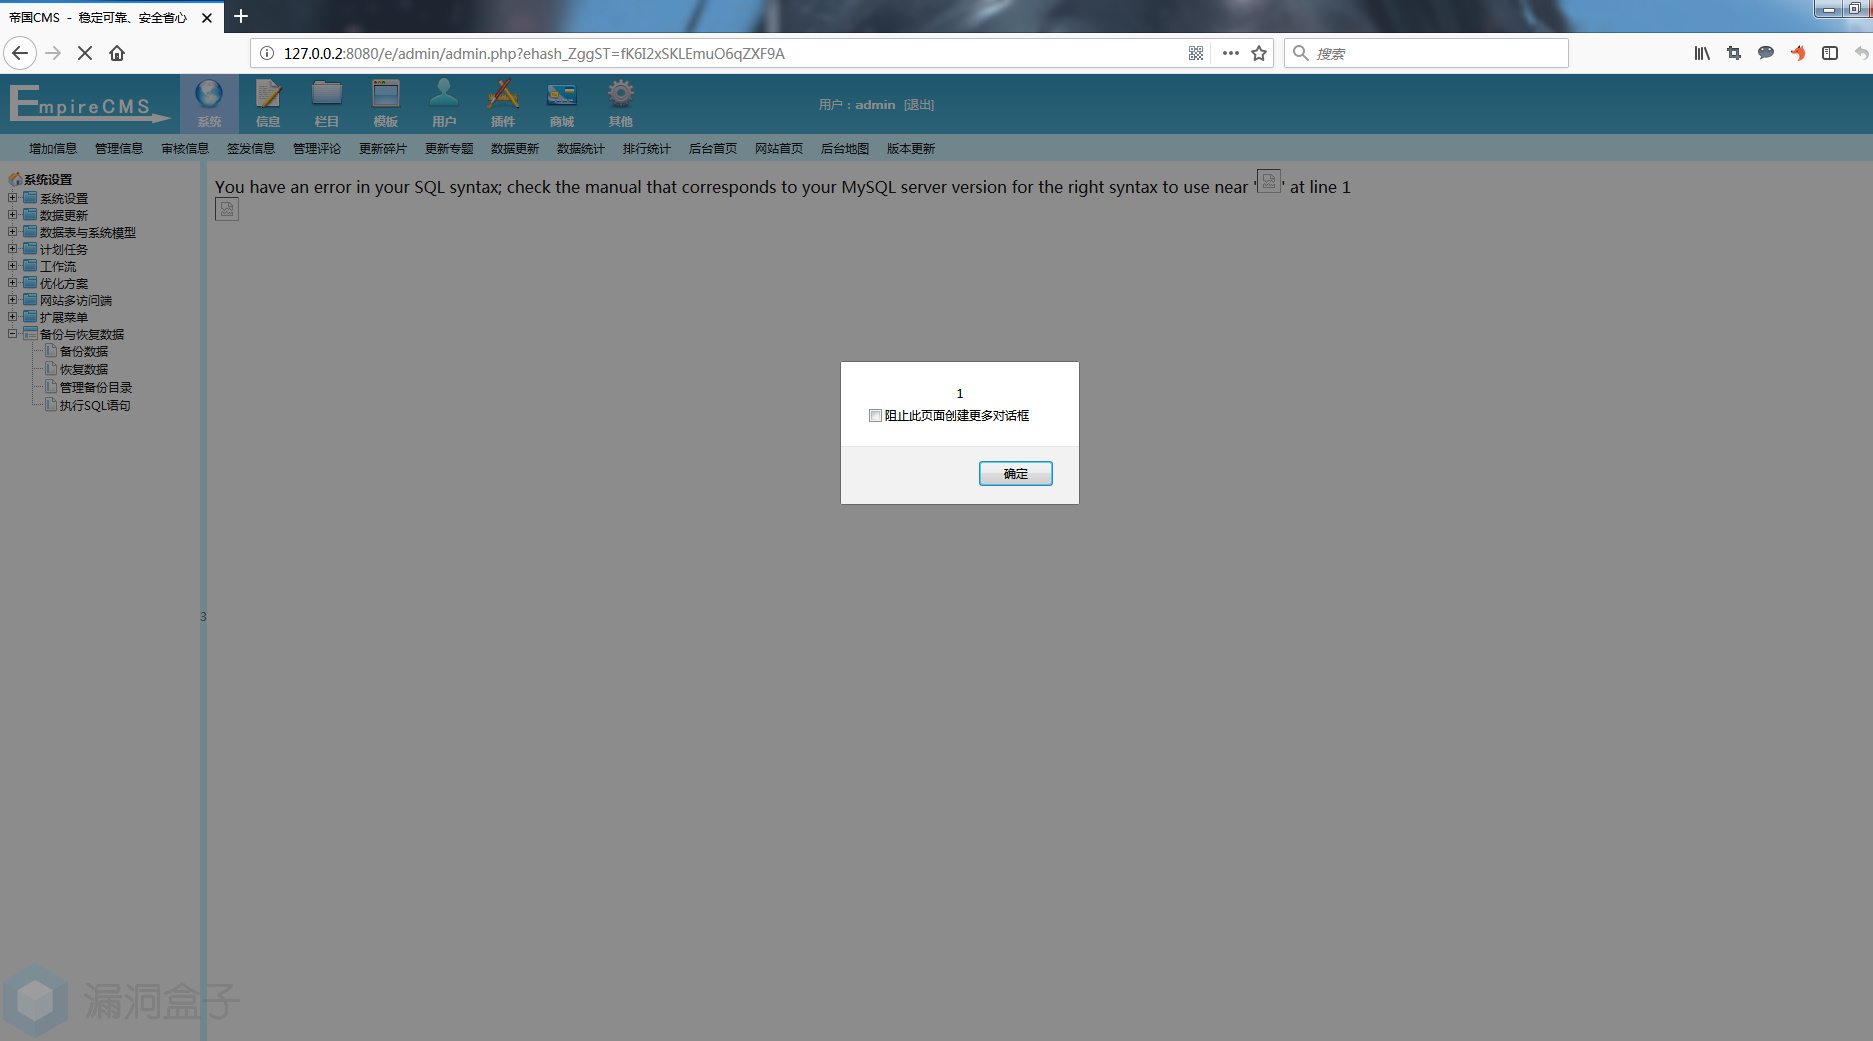
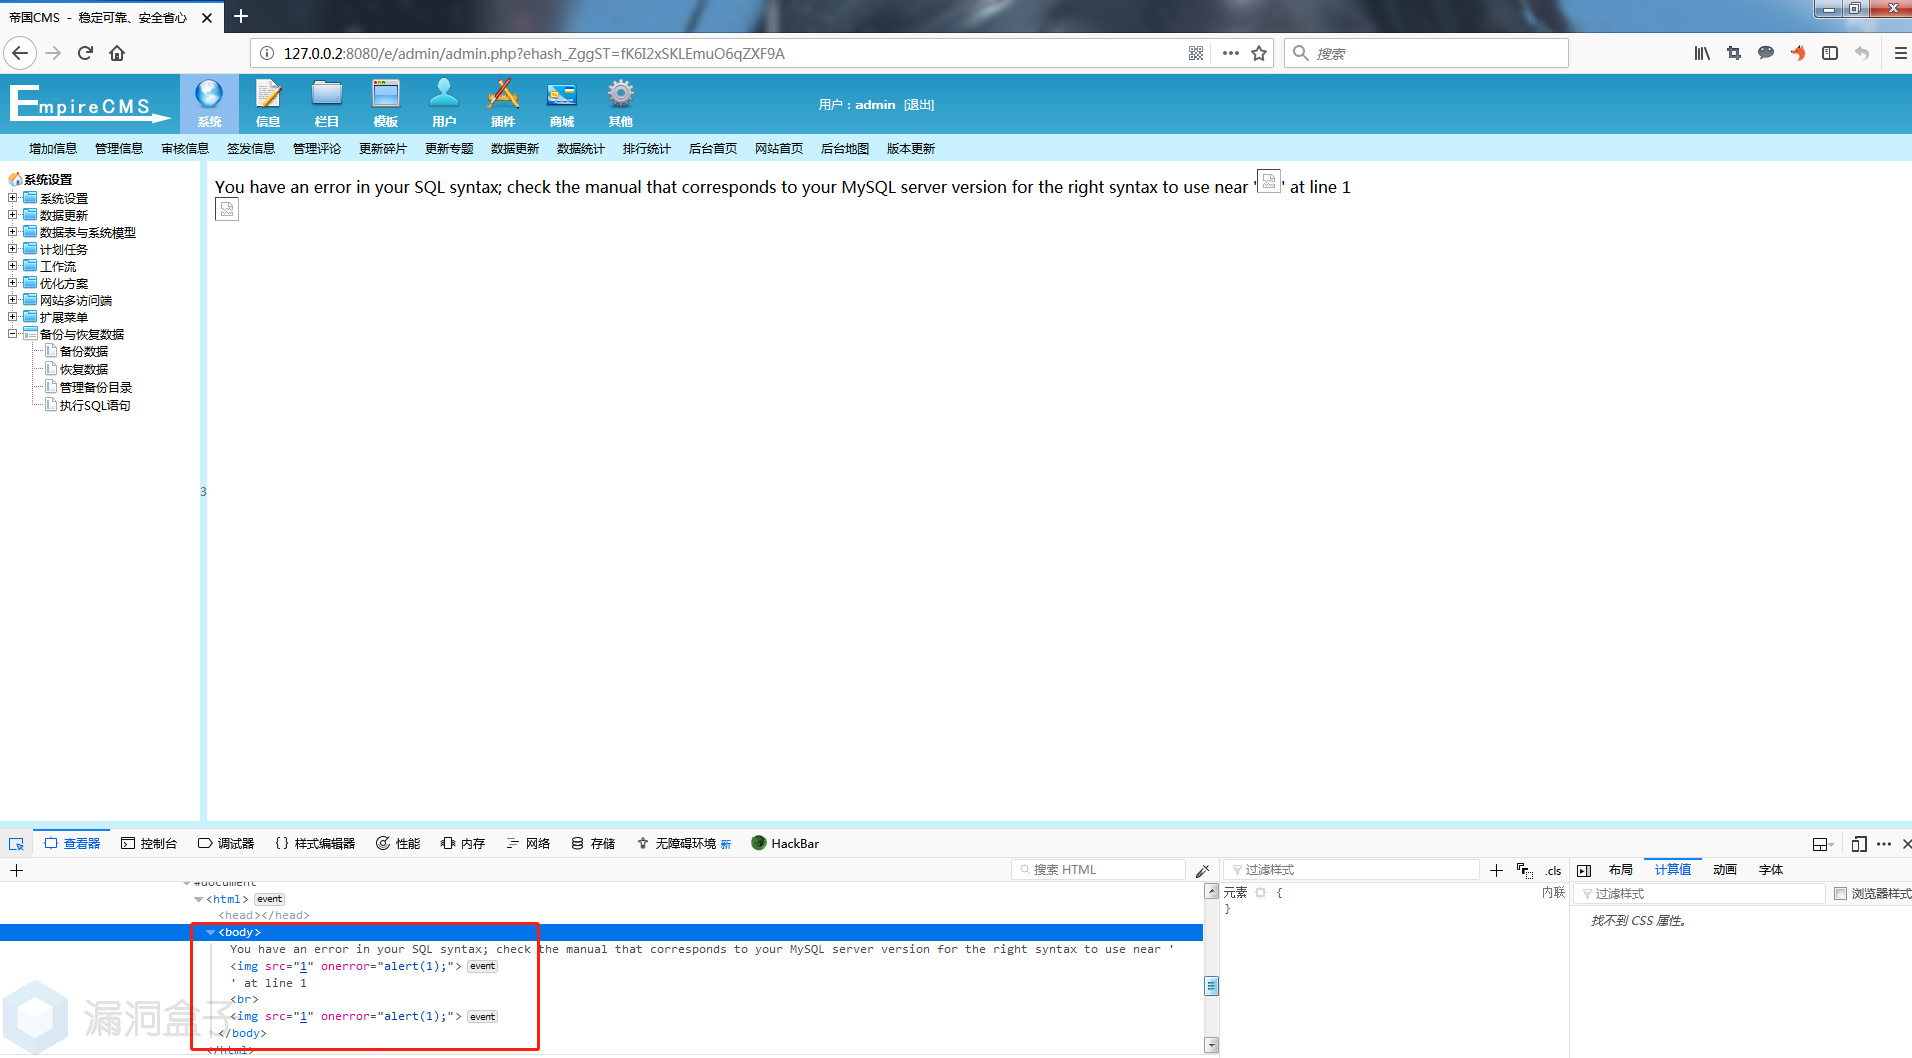
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
Attack profile
How easy it is to exploit
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- High
- User interaction
- Required
What an attacker can affect
- Confidentiality
- Low
- Integrity
- Low
- Availability
- None
Exploit likelihood
What each source reports
NVD Score used
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
- Record
CVE-2018-19461- CVSS 3.0
- 4.8 Medium
CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N - CVSS 2.0
- 3.5 Low
AV:N/AC:M/Au:S/C:N/I:P/A:N - Weakness
- CWE-79
- Updated
- 2026-11-02
CVE List No score
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
- Record
CVE-2018-19461- Updated
- 2026-11-02
EUVDEUVD-2018-11150 No score
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
- Record
EUVD-2018-11150- Updated
- 2026-11-03
GitHub AdvisoriesGHSA-f2vw-37xv-2cxr
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
- Record
GHSA-f2vw-37xv-2cxr- CVSS 3.0
- 4.8 Medium
CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N - Weakness
- CWE-79
- Updated
- 2026-11-02
Affected products
History
| Recorded | Changed | Sources |
|---|---|---|
| aliases | EUVD | |
| first indexed | CVE List, GitHub Advisories, NVD |
Dates are when Every CVE recorded each change. Upstream dates may differ.
In short
CVE-2018-19461 is a medium vulnerability (CVSS 4.8) in Phome Empirecms, published June 7, 2019. No source lists public exploit code. EPSS puts the chance of exploitation in the next 30 days at 0.92%, the 60th percentile. No source names a fixed version.
References
i.3001.net/uploads/Up_imgs/20181117-95a316d46f9a46dda7c48e541777d1fc.png%21small
github.com/novysodope/empireCMS7.5
nvd.nist.gov/vuln/detail/CVE-2018-19461