CVE-2018-19981
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS...
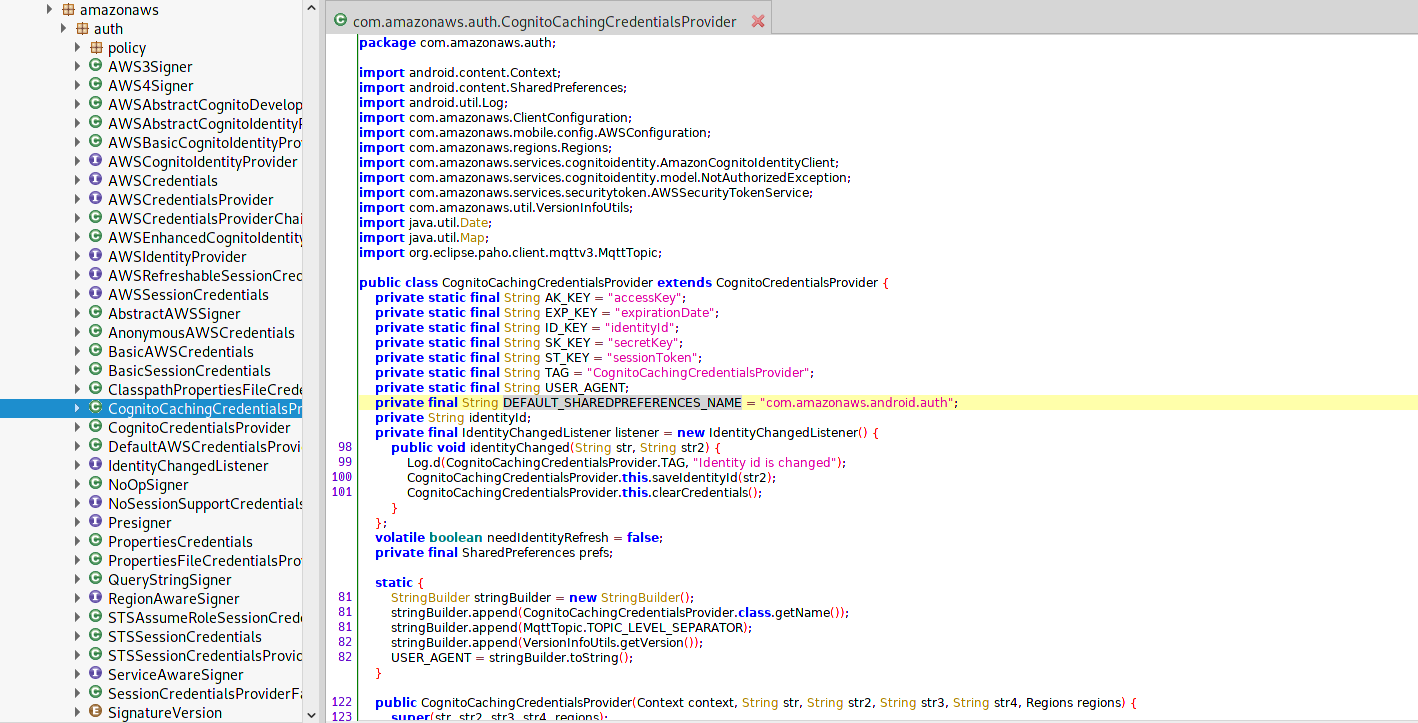
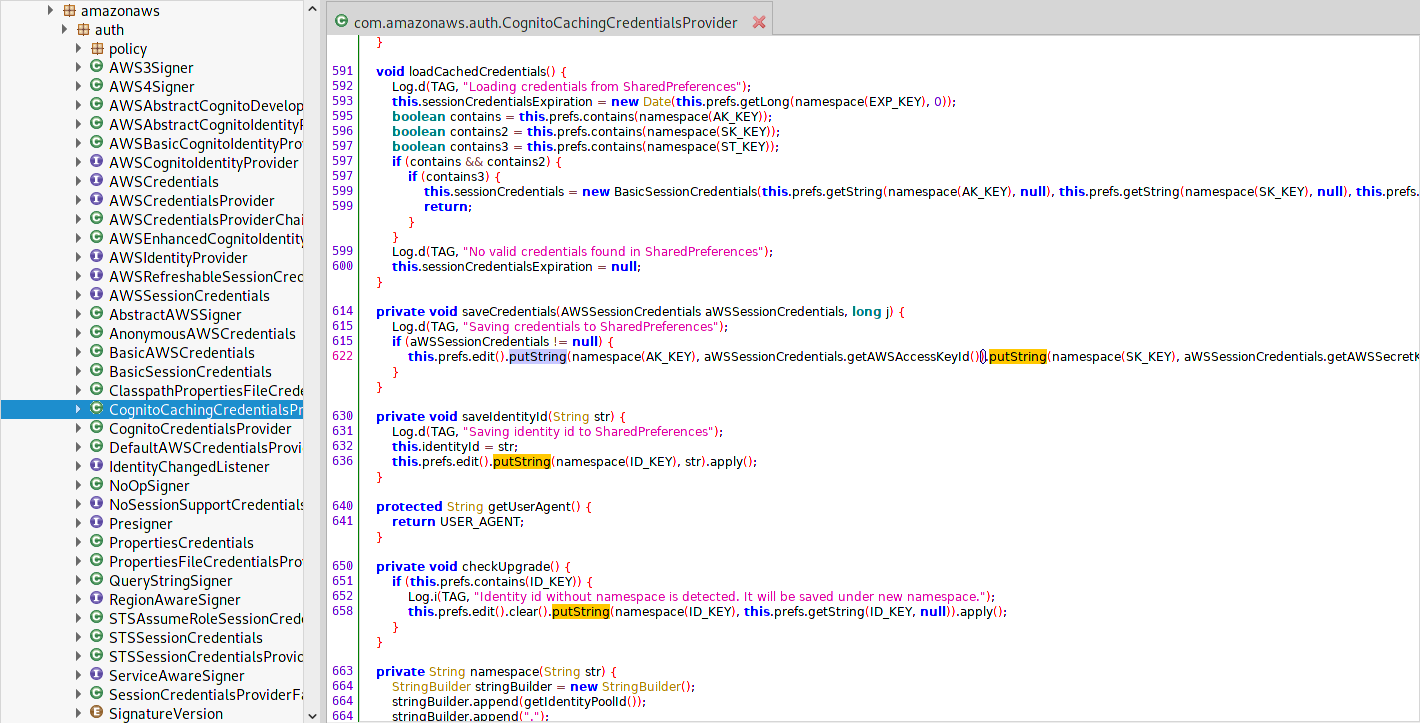
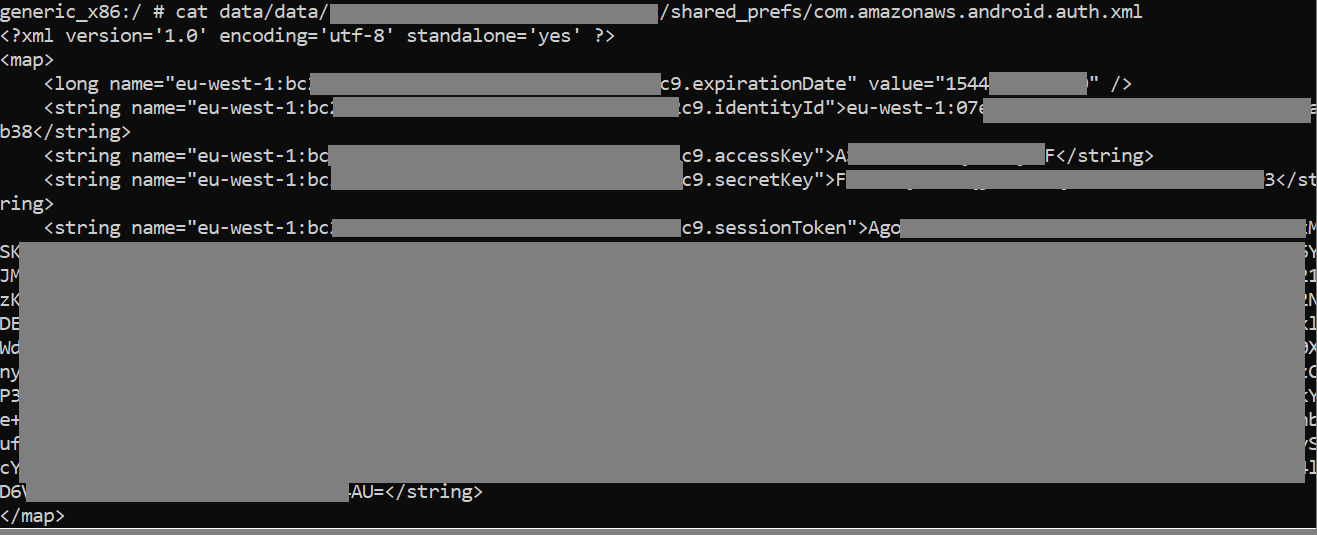
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
Attack profile
How easy it is to exploit
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- High
- User interaction
- None
What an attacker can affect
- Confidentiality
- High
- Integrity
- High
- Availability
- High
Exploit likelihood
What each source reports
NVD Score used
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
- Record
CVE-2018-19981- CVSS 3.0
- 7.2 High
CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H - CVSS 2.0
- 9.0 High
AV:N/AC:L/Au:S/C:C/I:C/A:C - Weakness
- CWE-312
- Updated
- 2026-11-02
CVE List No score
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
- Record
CVE-2018-19981- Updated
- 2026-11-02
EUVDEUVD-2018-11648 No score
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
- Record
EUVD-2018-11648- Updated
- 2026-11-03
GitHub AdvisoriesGHSA-4rp2-whvp-25jm
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS...
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
- Record
GHSA-4rp2-whvp-25jm- CVSS 3.0
- 7.2 High
CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H - Weakness
- CWE-312
- Updated
- 2026-11-02
OSV
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
- Record
CVE-2018-19981- CVSS 3.0
- 7.2 High
CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H - Updated
- 2026-11-02
Affected products
History
| Recorded | Changed | Sources |
|---|---|---|
| aliases | EUVD | |
| first indexed | CVE List, GitHub Advisories, NVD, OSV |
Dates are when Every CVE recorded each change. Upstream dates may differ.
In short
CVE-2018-19981 is a high vulnerability (CVSS 7.2) in Amazon Aws Software Development Kit, published April 4, 2019. No source lists public exploit code. EPSS puts the chance of exploitation in the next 30 days at 1.80%, the 78th percentile. No source names a fixed version.
References
raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_01.png
aws-amplify.github.io/aws-sdk-android/docs/reference/com/amazonaws/auth/CognitoCachingCredentialsProvider.html
nvd.nist.gov/vuln/detail/CVE-2018-19981
github.com/advisories/GHSA-4rp2-whvp-25jm