CVE-2026-8262
Devs Palace ERP Online chart-save cross site scripting
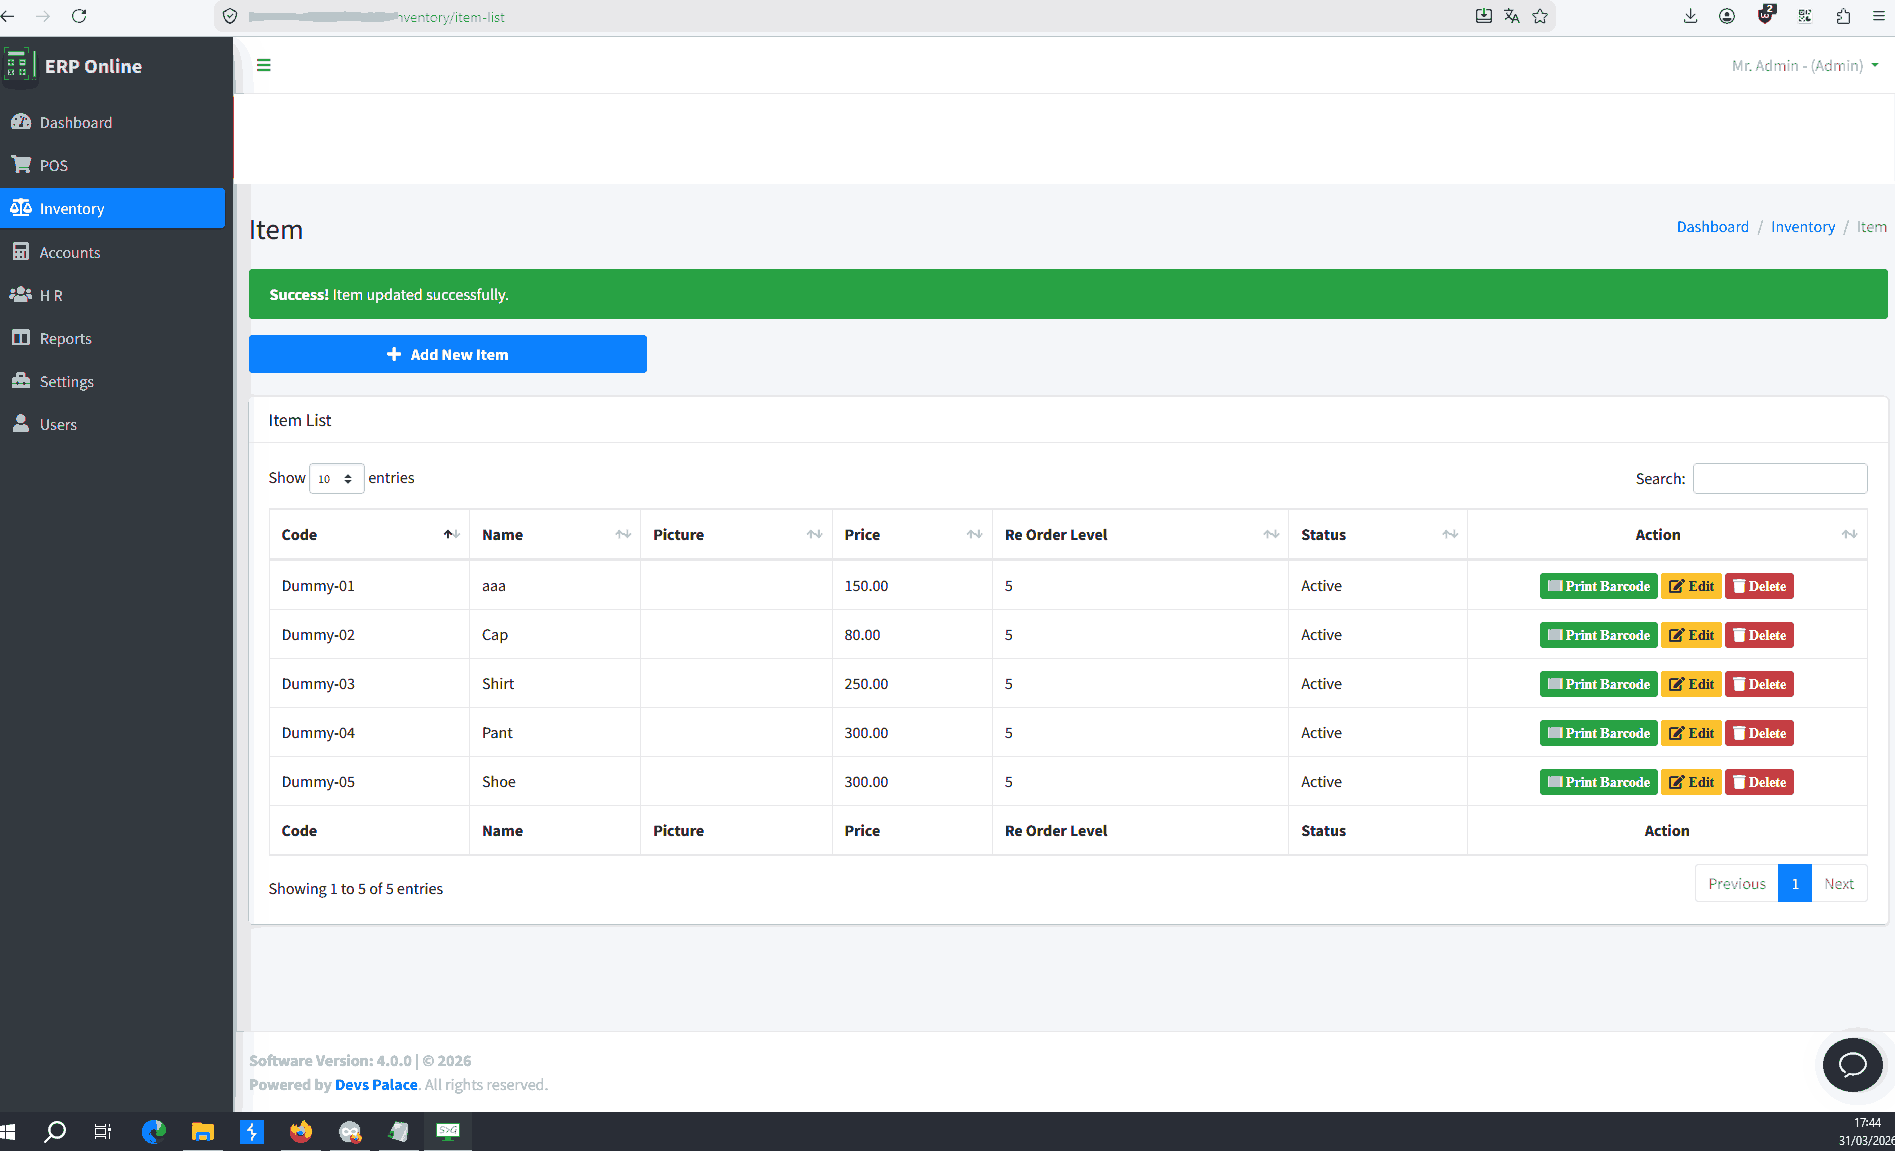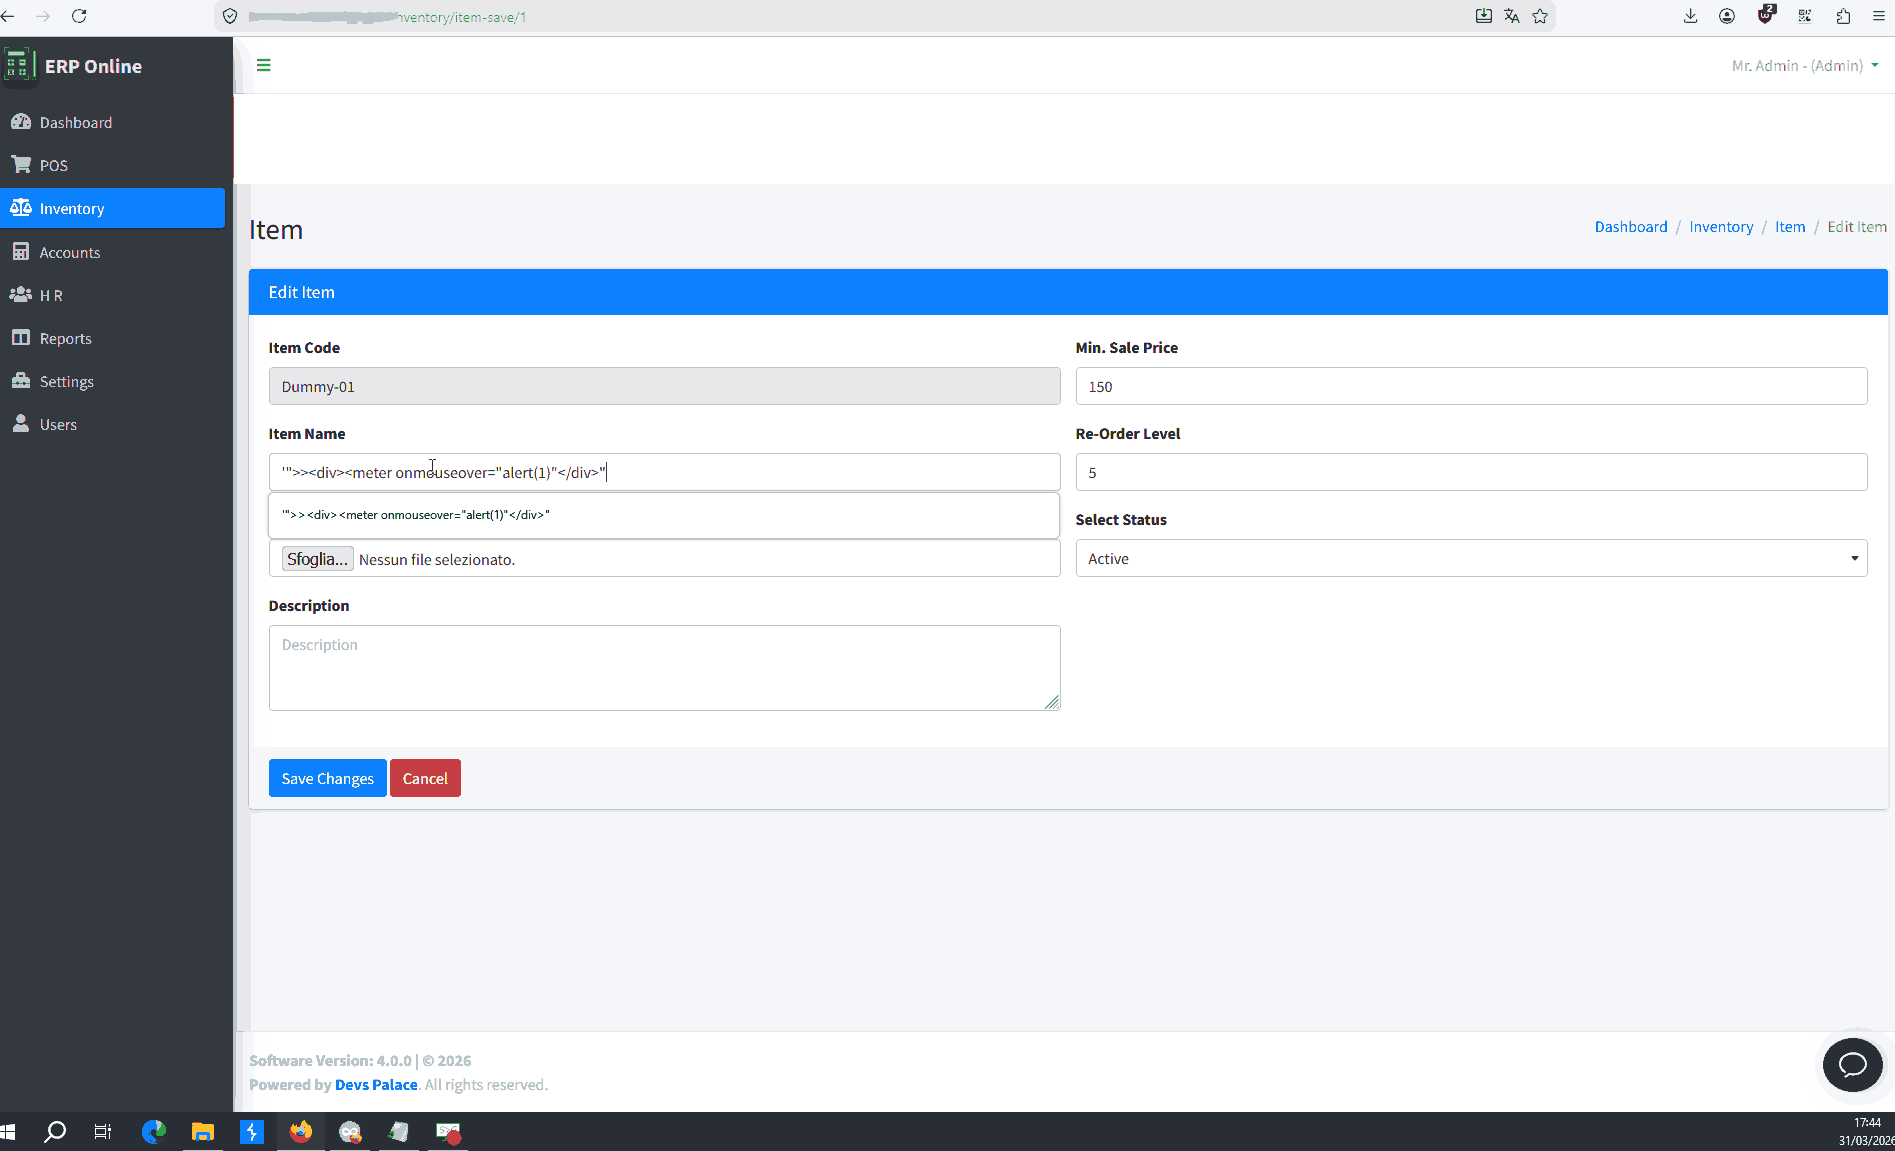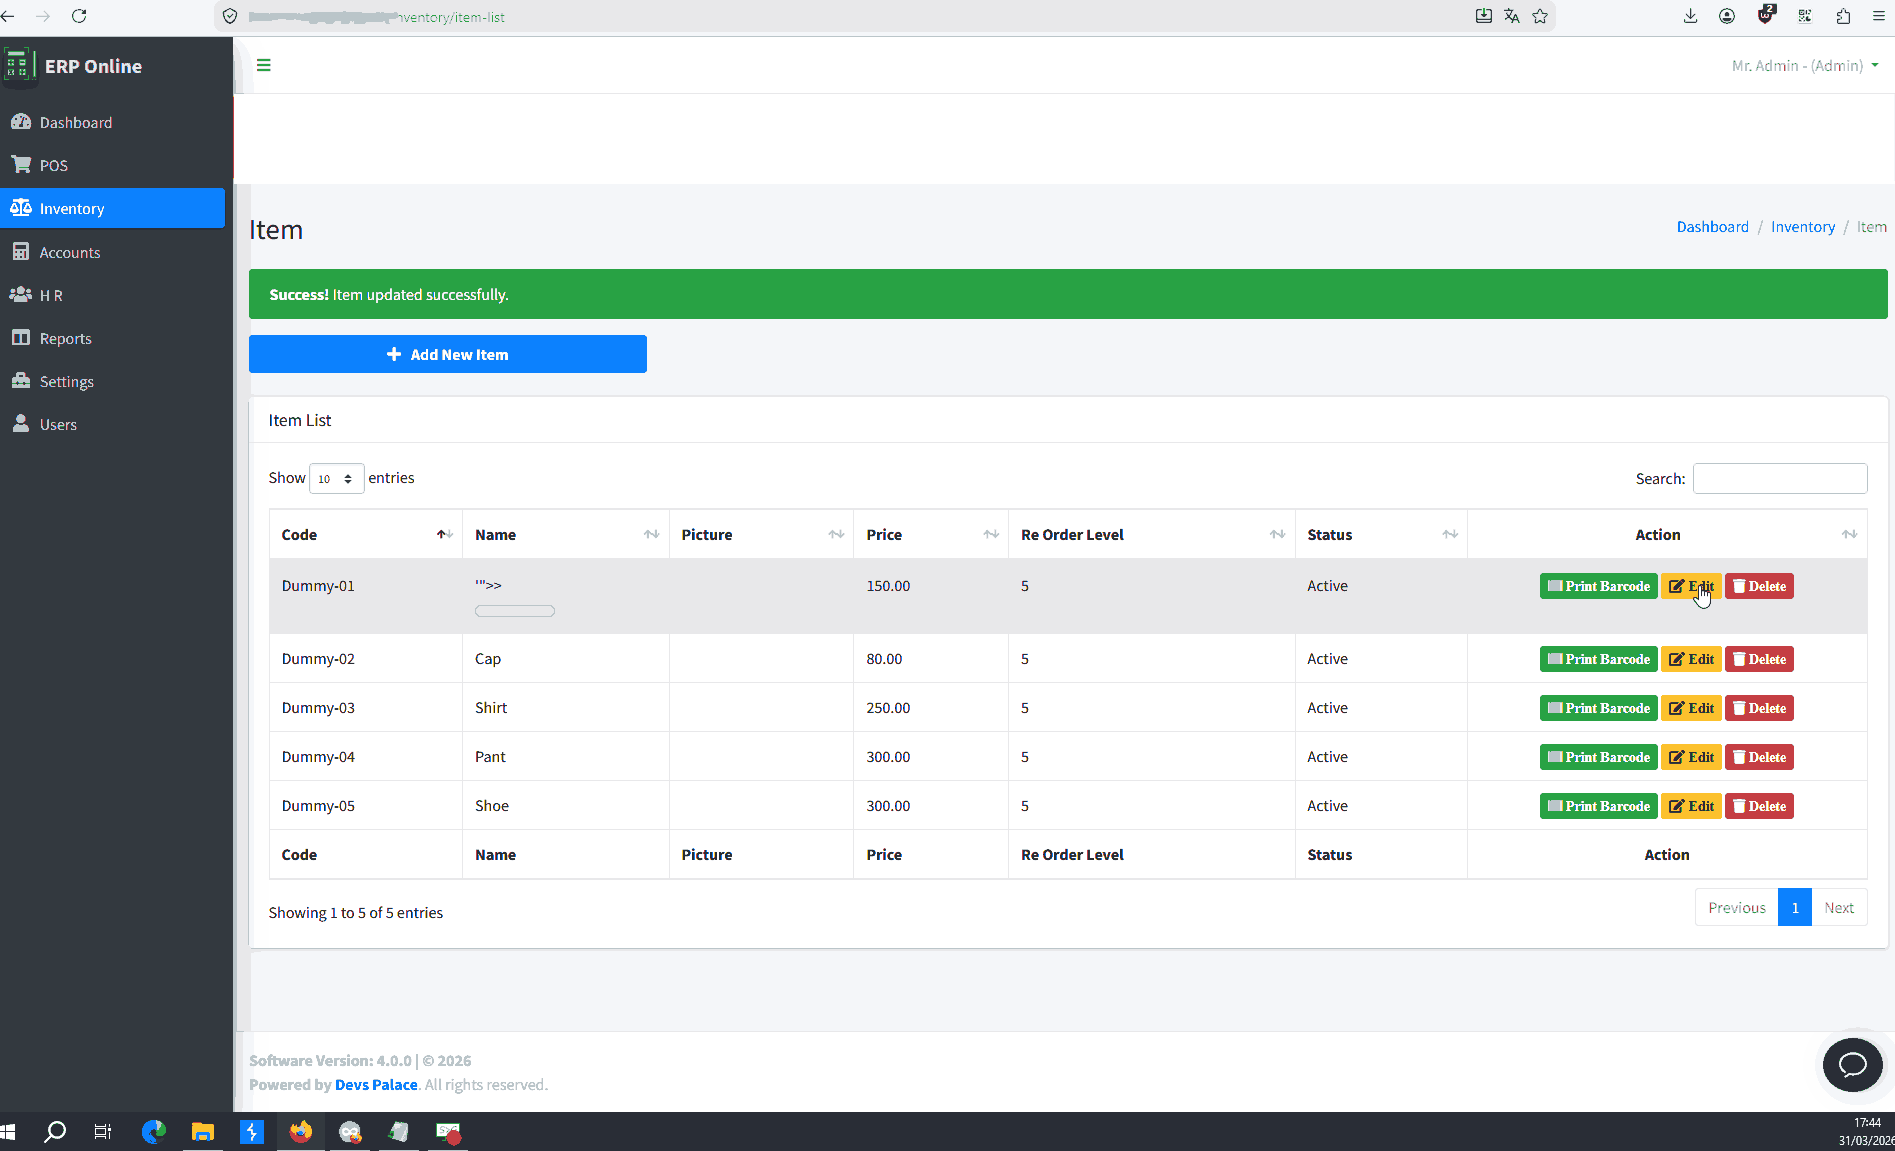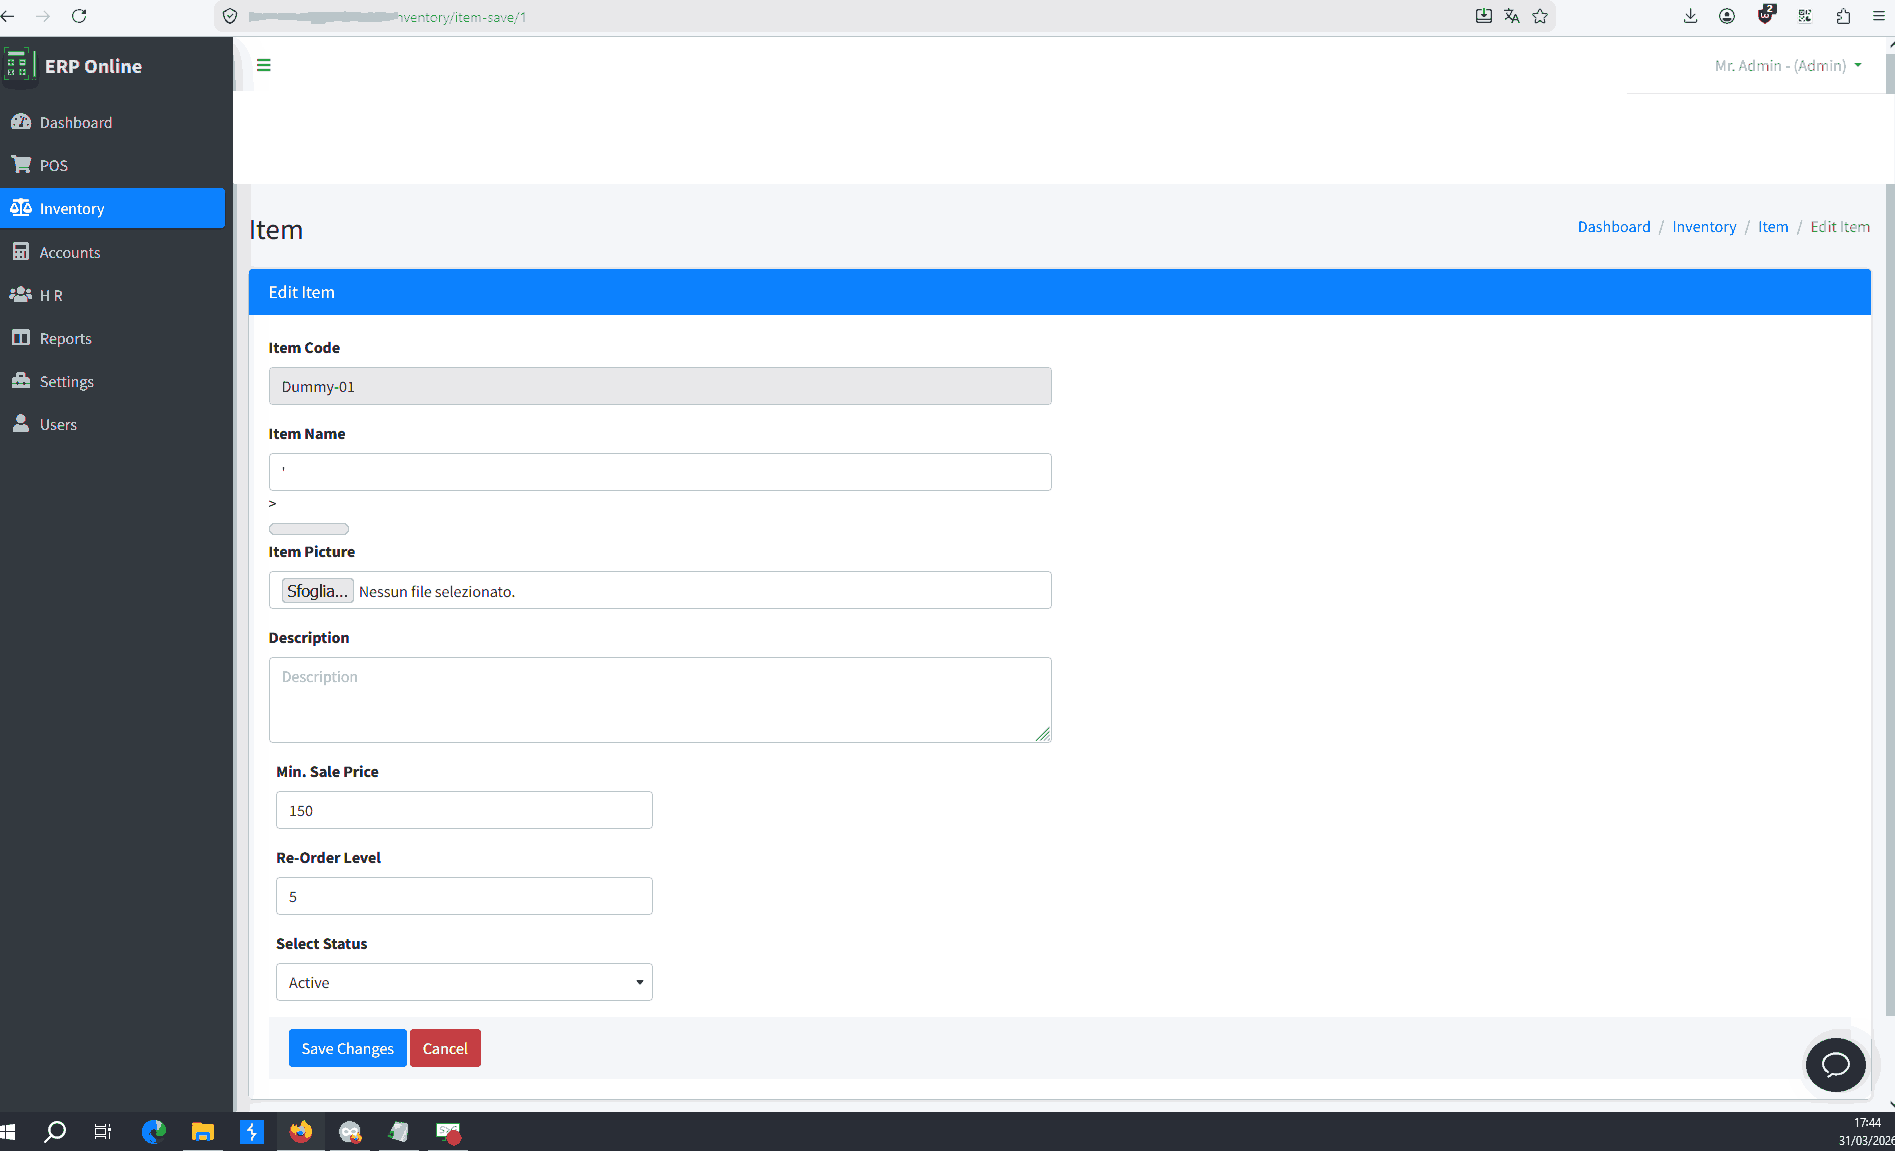
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /accounts/chart-save. Such manipulation leads to cross site scripting. The attack may be performed from remote. The exploit is publicly available and might be used. The vendor was contacted early about this disclosure but did not respond in any way.
Attack profile
How easy it is to exploit
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- High
- User interaction
- Passive
What an attacker can affect
- Confidentiality
- None
- Integrity
- Low
- Availability
- None
Exploit likelihood
What each source reports
CVE List Score used
Devs Palace ERP Online chart-save cross site scripting
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /accounts/chart-save. Such manipulation leads to cross site scripting. The attack may be performed from remote. The exploit is publicly available and might be used. The vendor was contacted early about this disclosure but did not respond in any way.
- Record
CVE-2026-8262- CVSS 4.0
- 4.8 Medium
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P - CVSS 3.1
- 2.4 Low
CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N/E:P/RL:X/RC:R - CVSS 3.0
- 2.4 Low
CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N/E:P/RL:X/RC:R - CVSS 2.0
- 3.3
AV:N/AC:L/Au:M/C:N/I:P/A:N/E:POC/RL:ND/RC:UR - Weakness
- CWE-79, CWE-94
- Updated
- 2026-11-02
EUVDEUVD-2026-29018
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /accounts/chart-save. Such manipulation leads to cross site scripting. The attack may be performed from remote. The exploit is publicly available and might be used. The vendor was contacted early about this disclosure but did not respond in any way.
- Record
EUVD-2026-29018- CVSS 4.0
- 4.8 Medium
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P - Updated
- 2026-11-02
GitHub AdvisoriesGHSA-xqwv-c88m-wq93
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown...
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /accounts/chart-save. Such manipulation leads to cross site scripting. The attack may be performed from remote. The exploit is publicly available and might be used. The vendor was contacted early about this disclosure but did not respond in any way.
- Record
GHSA-xqwv-c88m-wq93- CVSS 4.0
- 1.9 Low
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X - CVSS 3.1
- 2.4 Low
CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N - Weakness
- CWE-79
- Updated
- 2026-11-02
NVD
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /accounts/chart-save. Such manipulation leads to cross site scripting. The attack may be performed from remote. The exploit is publicly available and might be used. The vendor was contacted early about this disclosure but did not respond in any way.
- Record
CVE-2026-8262- CVSS 4.0
- 1.9 Low
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X - CVSS 3.1
- 2.4 Low
CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N - CVSS 2.0
- 3.3 Low
AV:N/AC:L/Au:M/C:N/I:P/A:N - Weakness
- CWE-79, CWE-94
- Updated
- 2026-11-02
Affected products
History
| Recorded | Changed | Sources |
|---|---|---|
| first indexed | CVE List, EUVD, GitHub Advisories, NVD |
Dates are when Every CVE recorded each change. Upstream dates may differ.
In short
CVE-2026-8262 is a medium vulnerability (CVSS 4.8) in Devs Palace Erp Online, published May 11, 2026. No source lists public exploit code. EPSS puts the chance of exploitation in the next 30 days at 0.20%, the 10th percentile. No source names a fixed version.